 CryptoChain Blog
Introduction to AI-Enhanced Hardhat Development
In 2026, securing Solidity smart contracts demands more than traditional manual processes. Developers now embed AI assistants directly into Hardhat workflows to speed up scaffolding, scanning, testing, and optimization while upholding strict security standards. This hybrid method merges Hardhat's established reliability with the rapid capabilities of contemporary AI models, allowing teams to handle increasingly complex decentralized applications without sacrificing audit readiness. Hardhat continues to serve as the primary Ethereum development environment, and its flexibility makes it ideal for AI integrations such as GitHub Copilot or custom bridges. Hardhat's official documentation supplies the core setup instructions that underpin these enhancements.
The benefits extend beyond speed. AI-augmented pipelines catch subtle vulnerabilities earlier, generate more thorough test coverage, and propose gas-efficient patterns that would take hours to identify manually. However, success requires disciplined validation to counter AI limitations like hallucinated code. This guide delivers hands-on instructions covering every stage from initial project creation through final deployment checks.
Setting Up Your Hardhat Environment with AI Tools
Begin by establishing a clean Hardhat project and layering AI capabilities. Install Hardhat via npm, then add extensions for Solidity support in your IDE. Configure workspace settings to enable inline suggestions from tools like GitHub Copilot. For advanced users, explore Foundry-AI bridges that allow custom model calls during Hardhat tasks. This foundation ensures AI assistance operates seamlessly within existing compilation and testing flows.
Practical steps include creating a dedicated .env file for API keys, installing necessary plugins through npm, and updating hardhat.config.js to register AI-related tasks. Test the integration by prompting the assistant for a basic contract template and verifying it compiles without errors.
AI-Assisted Project Scaffolding
AI dramatically accelerates initial project setup. After running npx hardhat init, use Copilot to generate folder structures, sample contracts, and deployment scripts tailored to your use case. Provide contextual prompts such as "Create a secure upgradeable ERC20 with role-based access control using OpenZeppelin contracts" to receive production-ready starting code.
Expand this by requesting configuration files for multiple networks, including testnet parameters and verification scripts. Review each generated file line by line before committing, then iterate with follow-up prompts to refine access modifiers or add events. This iterative scaffolding reduces setup time from hours to minutes while embedding security considerations from the outset.
Integrating Real-Time Vulnerability Scanning
Real-time AI scanning plugs directly into Hardhat's compilation pipeline. Plugins analyze code as you type or save, highlighting issues like unchecked external calls, improper access controls, or reentrancy risks. Configure the system to trigger scans automatically during hardhat compile tasks.
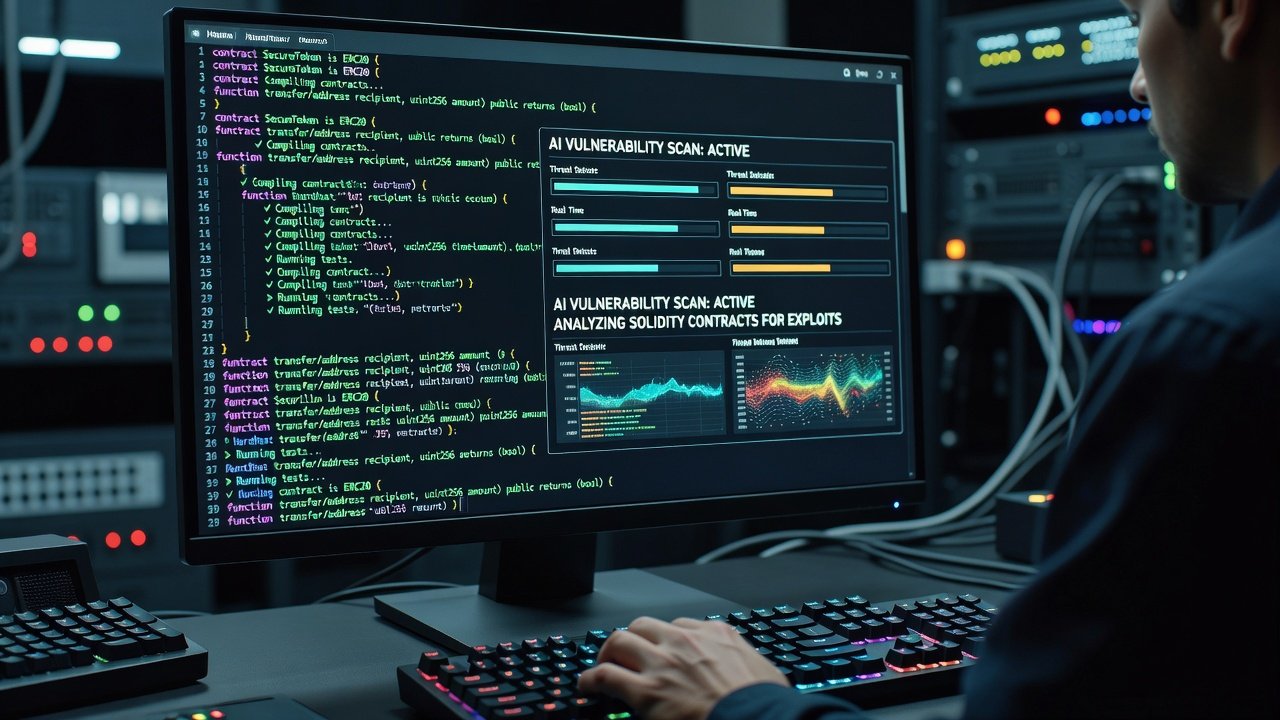
Setup involves installing the relevant Hardhat plugin, authenticating with your AI provider, and defining custom tasks that feed contract source into the model for immediate feedback. Results appear in the terminal alongside standard compiler warnings, allowing instant remediation. Over time, teams develop prompt libraries that target specific vulnerability classes common in DeFi protocols.
Automated Test Generation and Gas Optimization
AI excels at producing comprehensive test suites that cover edge cases developers might overlook. Prompt the assistant to create Mocha tests for every function, including fuzzing scenarios and invariant checks using Hardhat's network helpers. Generated tests often include negative cases for invalid inputs and boundary conditions.
For gas optimization, request suggestions such as packing storage variables, preferring calldata over memory, or implementing immutable constants where appropriate. Apply these incrementally and benchmark results using Hardhat's gas reporter plugin. Document each change to maintain an audit trail of AI contributions versus manual refinements.
Security Checklists and Attack Simulation Examples
Adopt a repeatable security checklist after accepting any AI-generated code:
- Confirm all state-changing functions include proper modifiers and event emissions.
- Validate external calls against reentrancy patterns using established guard clauses.
- Review arithmetic operations for safe math usage even when AI claims optimizations.
- Ensure upgradeability proxies follow the latest EIP standards when relevant.
Attack simulations provide concrete validation. Write Hardhat tests that impersonate accounts, execute flash-loan style sequences, or attempt unauthorized privilege escalations. Run these simulations in a forked mainnet environment to surface issues before any live deployment.
Addressing Common Pitfalls: AI Hallucinations and Validation
AI models occasionally produce plausible but insecure code. Hallucinations may include missing require statements, incorrect inheritance, or invented function behaviors. Counter this by routing every AI suggestion through static analyzers such as Slither integrated via Hardhat tasks. Combine automated scans with manual peer reviews and formal verification where contract value justifies the effort. Maintain version control branches specifically for AI experiments so changes can be isolated and rolled back easily.
Manual vs AI-Augmented Hardhat Pipelines
Manual workflows depend entirely on developer expertise and sequential manual reviews, frequently extending timelines and leaving coverage gaps. AI-augmented pipelines accelerate early phases including scaffolding and initial test creation while preserving the same rigorous final validation layers. The hybrid model delivers measurable improvements in test coverage density and vulnerability detection rates when paired with authoritative references from Solidity documentation and OpenZeppelin security resources. Teams report faster iteration cycles without increased risk when they enforce mandatory analyzer checks on all AI output.
FAQ on 2026 Best Practices
How do I validate AI-generated Solidity code reliably?
Combine Hardhat unit tests, static analysis tools, and formal verification before any deployment. Always maintain human oversight on critical logic.
Which AI tools integrate most effectively with Hardhat?
GitHub Copilot provides the strongest real-time assistance, while custom Foundry-AI bridges excel at task automation and batch analysis within Hardhat scripts.
What are the primary risks when using AI for smart contract development?
Key risks include hallucinated vulnerabilities and over-reliance without sufficient validation. Layered security processes remain essential regardless of tooling.
How should teams document AI contributions in audits?
Track AI-generated sections in separate commits and include analyzer reports showing that all suggestions passed validation before merge.
Conclusion
AI-powered Hardhat workflows mark a meaningful advancement in secure Solidity development for 2026. By implementing the structured approach detailed above, developers achieve faster delivery while reinforcing security fundamentals through disciplined verification. Continued refinement of prompts and validation routines will further strengthen these pipelines as AI capabilities evolve.
No comments yet. Be the first!